The process wall
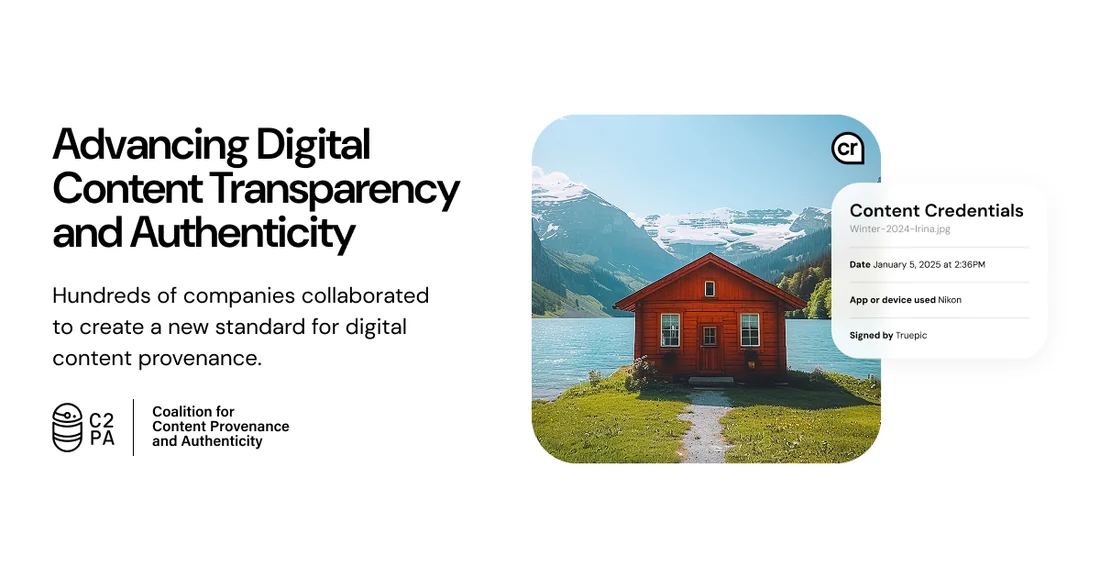
A maker exporting a finished image has, since 2022, had a specification to attach a record to it. The Coalition for Content Provenance and Authenticity, whose steering committee includes Adobe, Amazon, the BBC, Google, Meta, Microsoft, OpenAI, Publicis Groupe, Sony and TikTok, publishes a technical specification for what it calls a Content Credential, described on its own consumer-facing site as working 'like a nutrition label for digital content, giving a peek at the content's history available for anyone to access, at any time.' Retrieved on 16 September 2026, the specification is versioned rather than fixed to one date, and the coalition's stated aim is to give viewers a way to check origin and edit history rather than to prevent any particular kind of image from being made.
What the documents show
The specification itself defines a chain of small signed records: an assertion states a fact about an asset, who captured it, what tool acted on it, what changed; a claim gathers the assertions made by one actor at one time and signs them together; and where an asset incorporates earlier material, an ingredient manifest carries that earlier asset's own provenance forward, so a chain of edits can in principle be traced back through each tool that touched the file. Adobe's consumer-facing Content Credentials site frames the same mechanism as answering three questions for a viewer: what the content is, how it was made, and what has been done to it since.
Authorship and limitation
The specification names its own two structural limits plainly. First, participation is 'opt-in adoption': a credential only exists on an image if the capturing device or editing tool chose to write one, so its absence proves nothing about how an untagged image was made. Second, the specification explicitly permits an assertion to be dropped from later manifests when an asset is reused as an ingredient, and ordinary metadata stripping, a screenshot, a re-save through a tool that does not preserve it, removes the chain entirely. Content Credentials' own site acknowledges this directly, stating its goal is only 'to provide good actors with a way to demonstrate the authenticity of their content', not to stop a bad actor from presenting synthetic material as authentic.
What survives
What a maker can rely on is narrower than proof: a present, unbroken credential is evidence a device or tool recorded a specific claim at a specific step, checkable by anyone who inspects it, while its absence is not evidence of anything. Editorially, a credential is best read as a chain of tool-level claims rather than a verdict on authenticity.
- Open an image's Content Credential, where present, and check which tools appear in its ingredient chain.
- Check whether an editing tool in your own workflow writes or strips C2PA data on export.
- Ask whether a claimed 'verified' badge reflects a signed manifest or only a platform's own unlinked assertion.
A specification this widely adopted by name still depends on every tool in a chain choosing to participate, which is a governance question the documents leave open rather than resolve.
Sources & reading trail
States the coalition's membership and describes a Content Credential as a viewer-facing record of a content item's history.
Source published: Not established · Retrieved: 16 September 2026
Defines assertions, claims and ingredient manifests, and states that adoption is opt-in and that assertions can be removed when an asset becomes an ingredient.
Source published: Not established · Retrieved: 16 September 2026
States the credential's purpose for viewers and the stated goal of helping good-faith actors demonstrate authenticity rather than stopping bad-faith mislabelling.
Source published: Not established · Retrieved: 16 September 2026
Papers, documentation, rulings and the makers' own records establish the note; the authorship reading and what-survives are Creative AI editorial analysis. This retrospective draft does not imply the site published on the event date.